Phnom Penh, Cambodia

SoksambattSar

Cybersecurity enthusiast
Ethical Hacker & Penetration Tester
Community builder helping rural areas through charity work.

Read on
Portrait of Soksambatt Sar
Environment // Python Linux Bash PowerShell VBS C++ Git Docker Nginx

Ethical Hacker & System Specialist

I operate at the intersection of security research, automation, and system administration. My work centers on identifying vulnerabilities before malicious actors do, building security tooling, and streamlining operations for dynamic environments.

Beyond technical assessments, I am deeply involved in community development—organizing charity initiatives and driving technical engagement in rural communities across Cambodia. Whether performing penetration testing or building defensive tools, my objective is always long-term reliability and positive real-world impact.

[Operations]

Select to expand

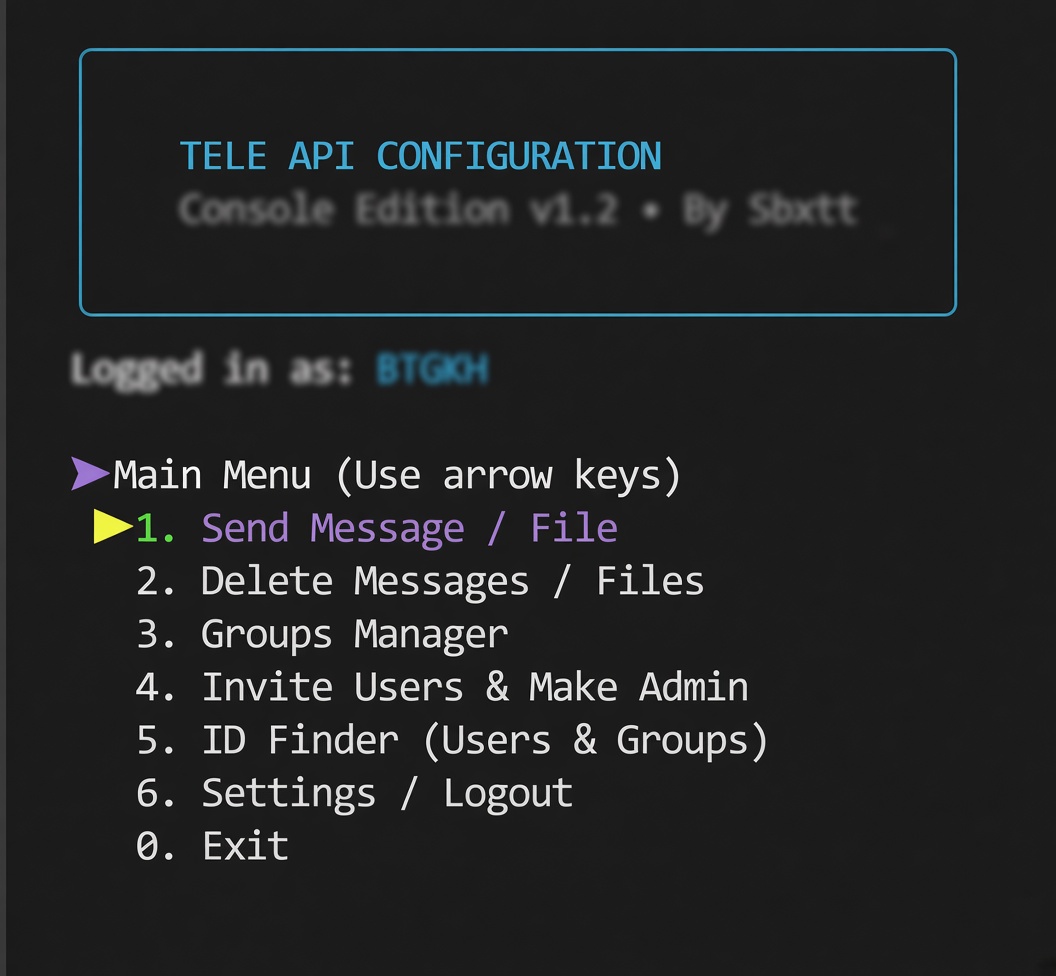
Telegram API Console is a powerful Telethon-based tool that uses your Telegram API ID and API Hash to give you full control over your account.

With this tool you can:

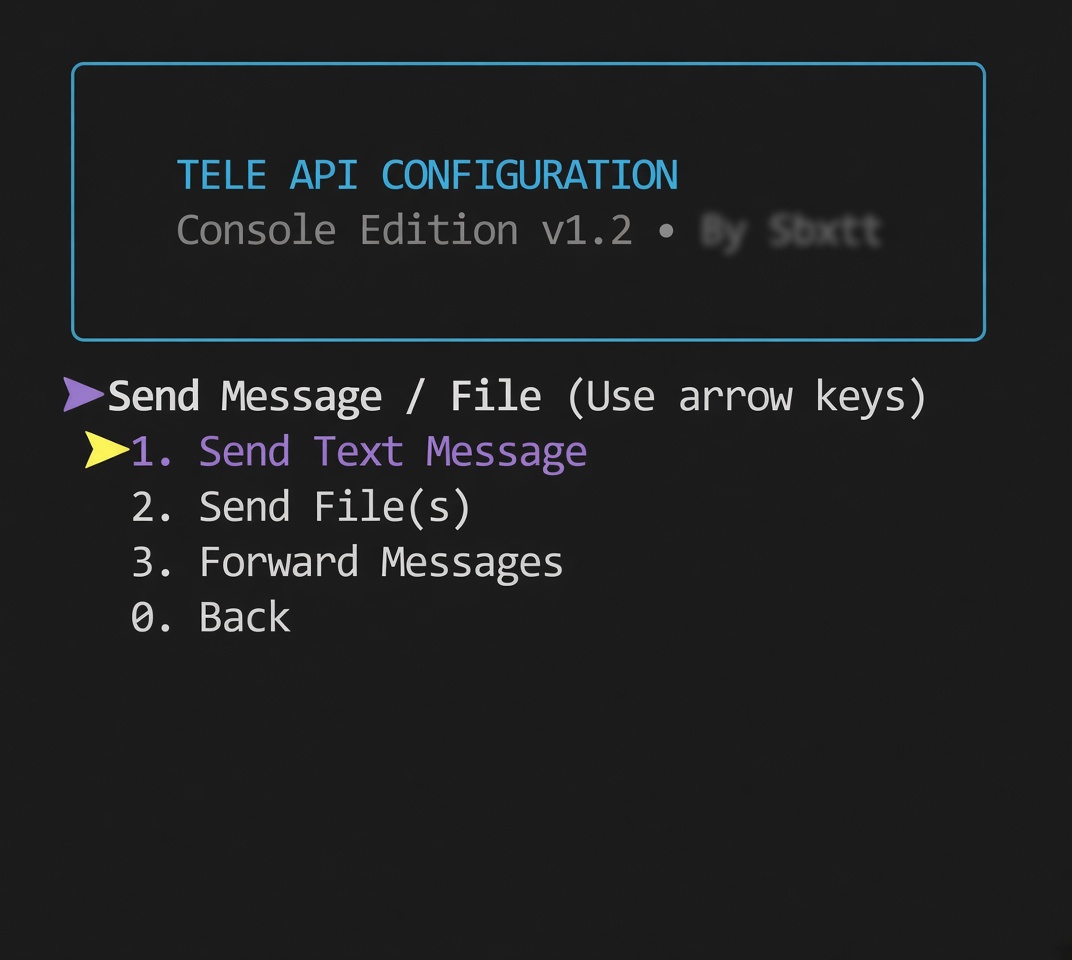
  • Send text messages, files, or forward content to multiple users and groups at once
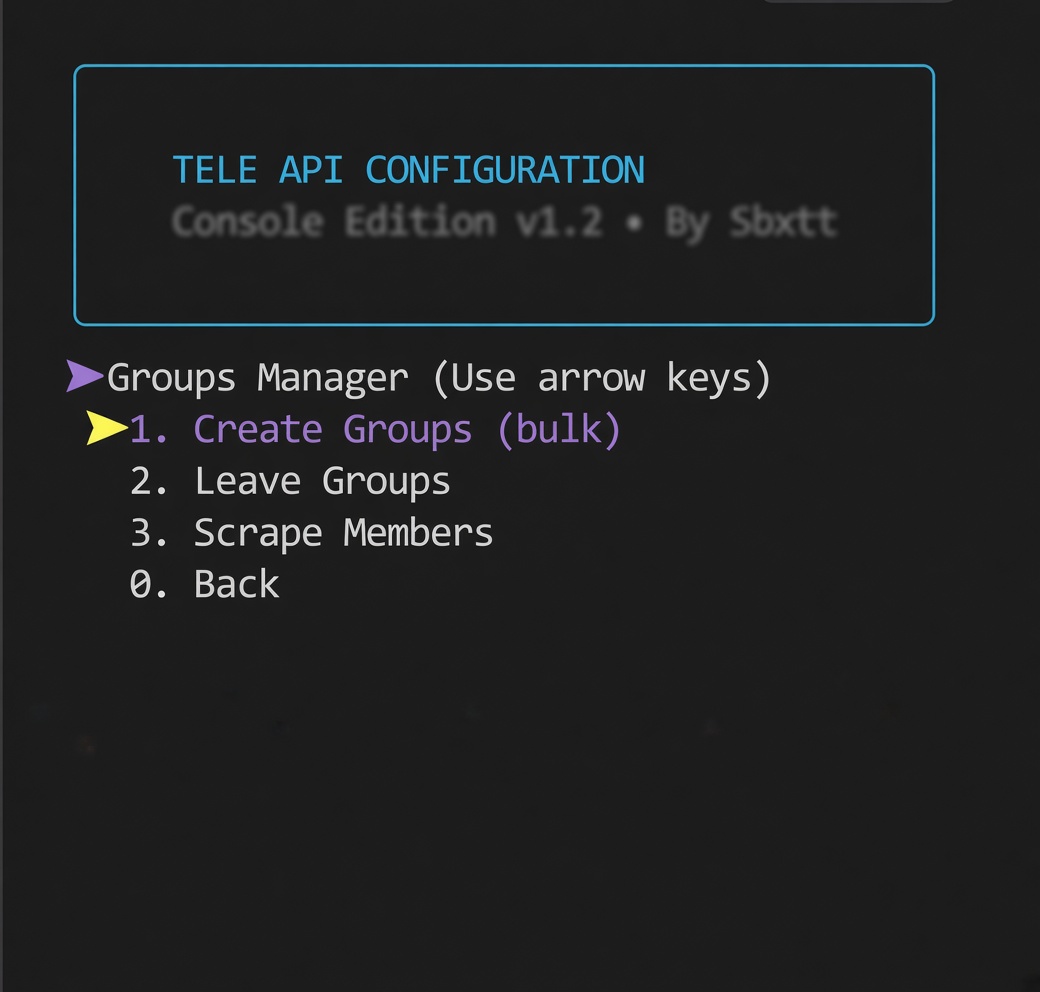
  • Create and leave multiple groups in bulk
  • Scrape member information from any group you're in
  • Invite multiple users to a group and promote them to admin in one go
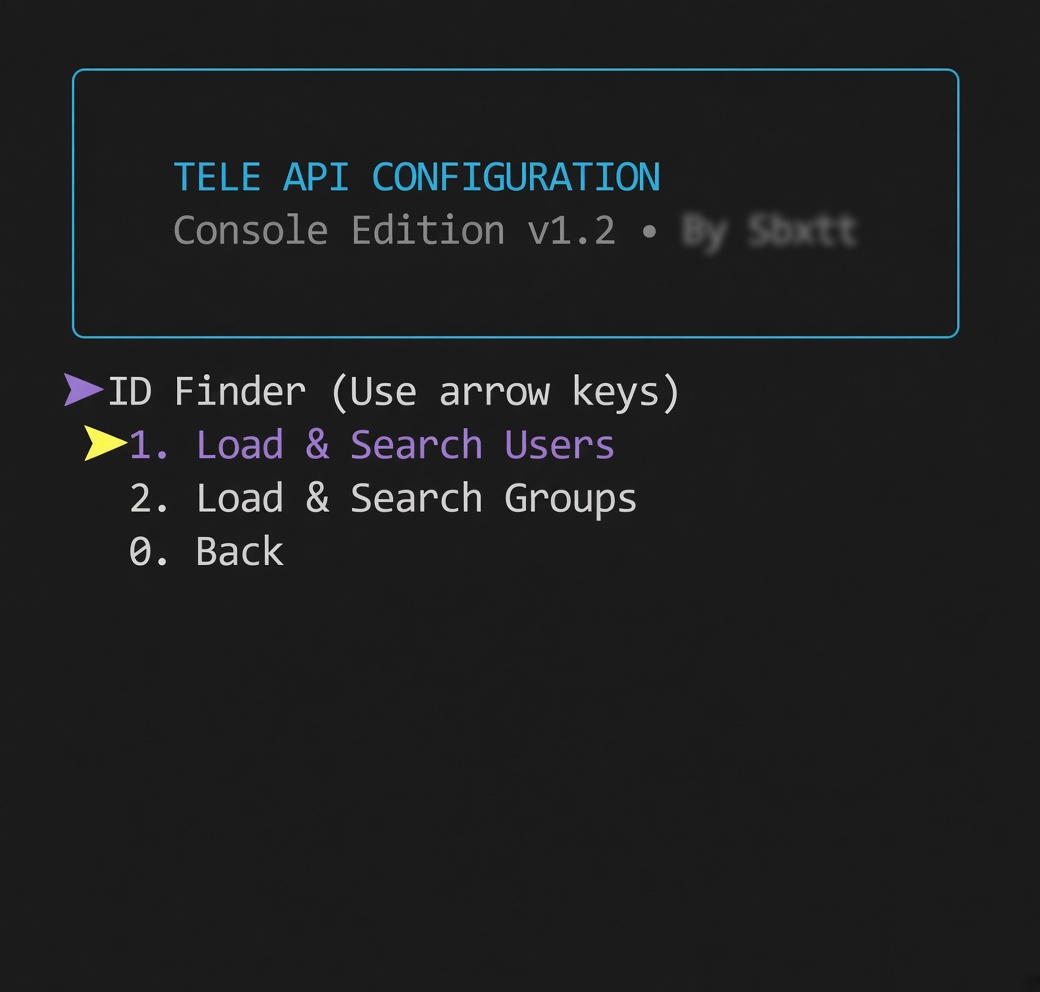
  • Find and view user IDs from your conversations, contacts, and groups
  • Instantly delete multiple messages you've sent
  • (What you saw is only part of the menu)

telethon_core.py
Private Source
# Telethon Async Operator (Sanitized Preview)
from telethon import TelegramClient, errors, functions, types
from telethon.tl.types import UserStatusOnline, UserStatusOffline, UserStatusRecently, UserStatusLastWeek, UserStatusLastMonth

nest_asyncio.apply()
console = Console() 

class TeleConsole:
    def __init__(self):
        self.client = None
        self.api_id = None
        self.api_hash = None
        self.phone = None
        self.is_running = False
        self.full_users_data = []
        self.full_groups_data = []

Perfect for anyone who regularly messages many customers or needs to send reminders to large numbers of people — all with just a few clicks.
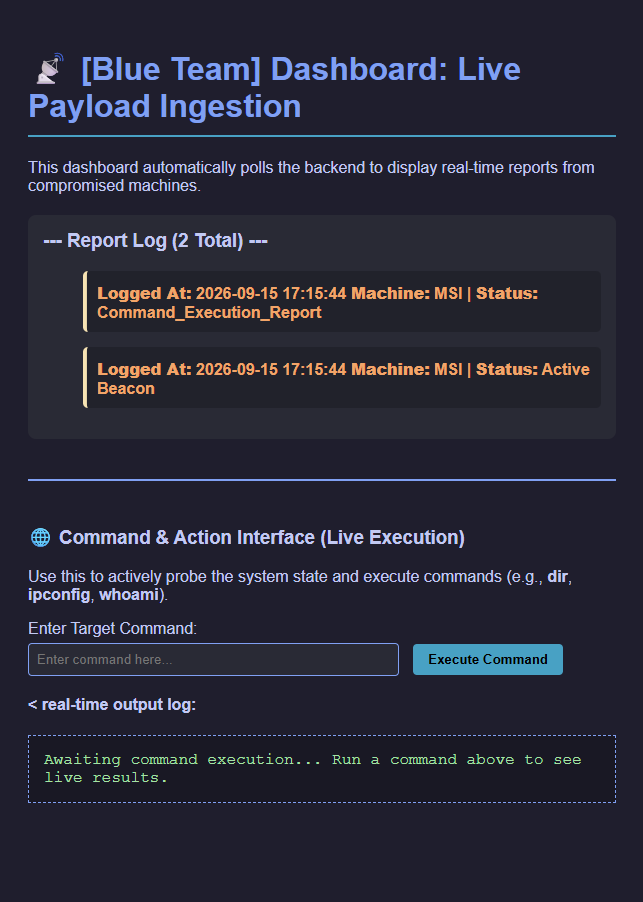
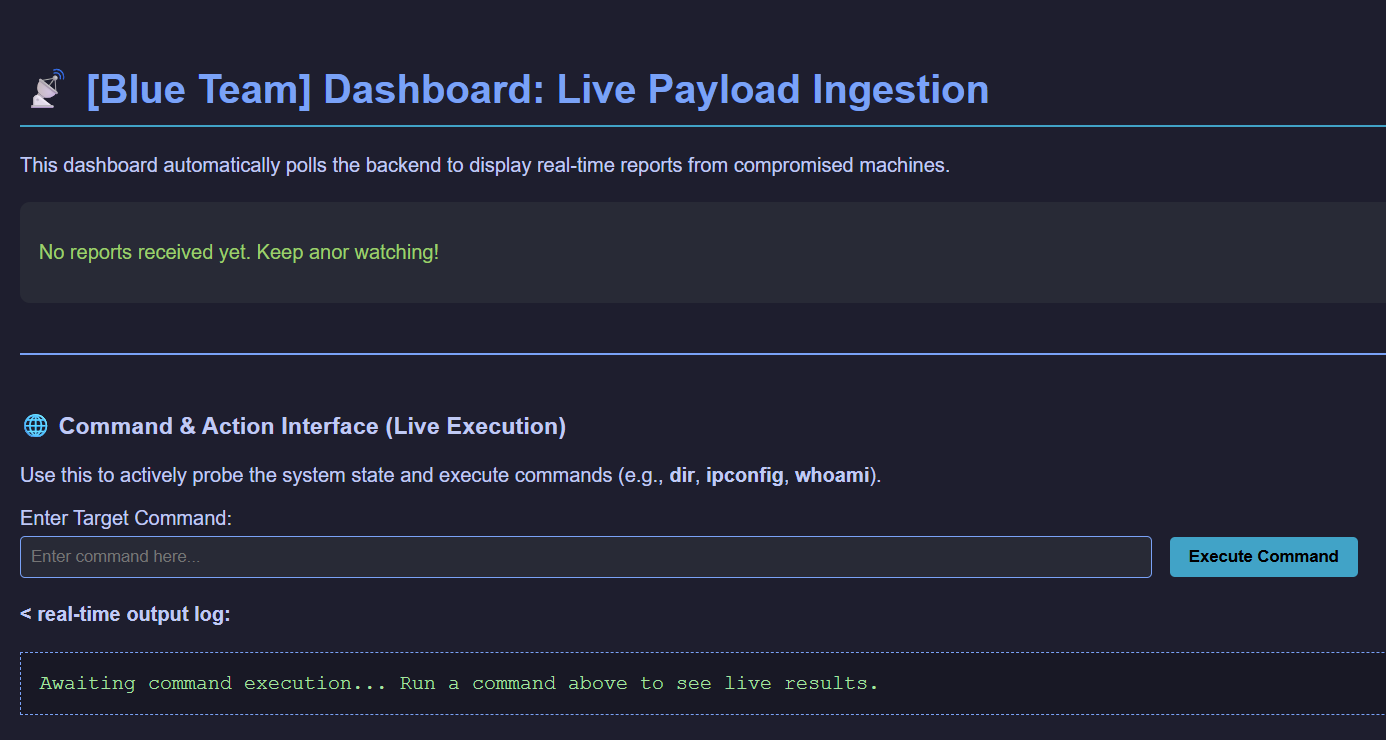
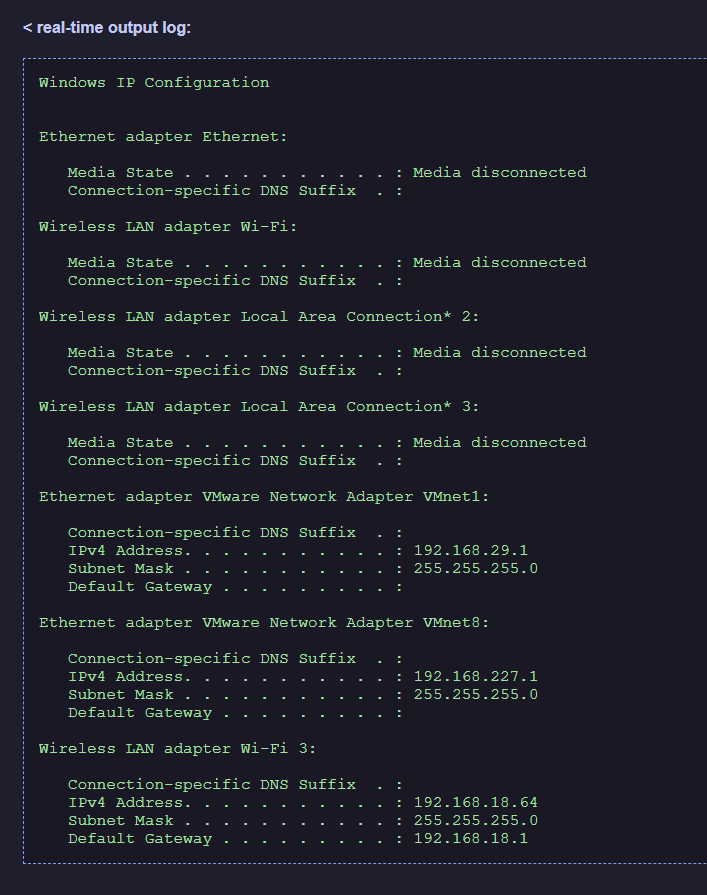
This project simulates a full attack chain in a controlled lab environment, from initial execution through post-exploitation, to demonstrate how a target system can be compromised without any user interaction beyond opening the payload. Once triggered, the script quietly establishes a background service and registers a scheduled task so the implant persists and re-launches automatically even after the target machine restarts. The implant then beacons out to a cloud-hosted listener, giving the operator console a live view into the target's file system and the ability to issue commands remotely. The dashboard above shows the operator's view of an active session, the session metadata collected from the target, and a live command being executed against it — illustrating the kind of persistence, stealth, and remote-control techniques this project was built to explore and defend against.

This method requires a lot of effort to set up these operations, since it involves a lot of moving parts — each step needs careful analysis and revision. This C2 combines multiple programming languages (PowerShell, Python, HTML & CSS) to operate efficiently.

Will be add soon in no time!

update soon...!